ID.me Authenticator

- 11.33K Reviews
- 3.5
- Downloads
- 5,000,000+
Our take on ID.me Authenticator from Appgk
Two-factor authentication is one of those small security habits that only feels important when a login suddenly depends on it. I tested ID.me Authenticator with that practical reality in mind: not as a flashy productivity tool, but as a companion app you open briefly when another service asks for an additional verification step. Its purpose is narrow, and that is mostly a strength. You are not dealing with a crowded dashboard or a collection of unrelated tools; you are using an app from ID.me intended to help confirm that a sign-in request is really yours.
The app is free, aimed at everyone, and available for Android devices running version 6.0 or later. It has been around since December 11, 2018, and its current version is 1.12.0-2025082916. That long presence helps explain why it has become a familiar option for people who need an authenticator rather than a full password manager. With more than five million installs, it is clearly used beyond a small technical audience, although its average rating of 3.5 from roughly seventy-three thousand ratings suggests that the experience is not equally smooth for everyone.
Where the real friction appears
The first thing I would tell a new user is that an authenticator app does not replace the account or service you are trying to access. It is one part of the login process. That distinction matters because many apparent app failures are actually caused by an incomplete account setup, a wrong verification method, or a sign-in page waiting for a different kind of approval.
When a website or service asks for a code, the usual mistake is to expect the app to know which account is being accessed without any earlier connection. The app needs to be paired with the relevant sign-in system first. If that pairing was skipped, interrupted, or completed with the wrong account, opening the app alone will not repair the login. I found it more useful to treat the authenticator as a key that must first be registered, not as a universal inbox for every security request.
Best Parts of ID.me Authenticator
Things to Keep in Mind About ID.me Authenticator
Another common sticking point is timing. A verification code can be short-lived, so entering an old code after switching between apps may fail even when the app is working normally. I recommend opening the login page first, moving to ID.me Authenticator only when the page requests the second step, and returning promptly to enter the current code. This simple order reduces the chance of copying a code that has already changed.
The most important habit is to identify which screen is responsible for the next step. If the app shows a code but the website rejects it, check the account and login page before repeatedly generating new attempts. If the app does not show what you expected, return to the service’s security settings and confirm that this is the authenticator method actually selected for the account.
News and Features Related to ID.me Authenticator

News
YouTube Turns a Quick Video Check Into an Hour of Watching

News
BeautyPlus Makes Portrait Retouching Feel Like Your Own

News
TikTok’s Effortless Feed Makes Every Swipe Count—and Every Mistake Harder to Undo
What to check before blaming the app
Before setting anything up, I would make sure I am signed into the intended account in the service that requested authentication. This sounds obvious, but it is easy to have a personal account open in one browser tab and a work, government, or benefits-related account open in another. An authenticator code is useful only when it belongs to the same account and security setup as the login attempt.
I would also avoid changing several things at once. If the login is failing, do not immediately uninstall the app, clear every browser session, and start a new registration. That can remove the trail needed to understand where the mismatch occurred. A slower check is safer: confirm the account, confirm the selected authentication method, then try one fresh login.
Don't want to read the full review?
Because the app is designed for a focused security task, its value depends on reliability at the moment you need it rather than on how often you browse it. I like that limited role, but it also means the app cannot solve a locked account, a rejected identity check, or a service-side problem. It can provide the authentication step; it cannot decide whether the main service should accept your account.
Setting it up without creating a future problem
The setup deserves more attention than the everyday use. Once the authenticator is connected correctly, checking a code is usually a short action. The risk is making a rushed connection and discovering later that the account, device, or recovery path is not what you expected.
Screenshots
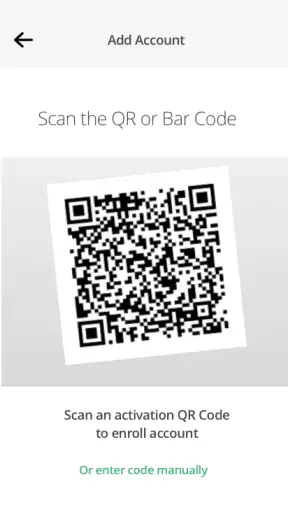
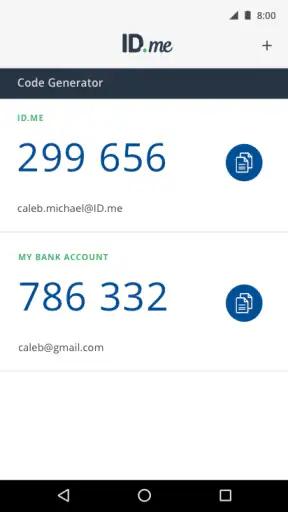
I would begin from the account’s own security or sign-in settings rather than opening the authenticator and guessing what to do next. Follow the service’s instructions until it specifically asks you to use an authenticator. Then complete the pairing shown there and verify the result with a fresh login while the original session is still available. This gives you an immediate test instead of assuming the setup worked because the app opened.
That test is especially useful if you use several accounts. Give yourself a moment to distinguish them clearly during setup. If the app presents more than one entry, do not select the first one automatically. Match the account identity shown by the service with the entry you intend to use. A code from the wrong entry can look perfectly valid while still being useless for the current login.
I also recommend keeping the phone in a usable state before beginning. Make sure the device can open the app, switch back to the login screen, and display the current code clearly. Avoid beginning account recovery or security changes when the phone is nearly unusable, the browser session is unstable, or you are about to leave the network area. The authenticator itself may be simple, but the surrounding workflow can be delicate.
One practical trade-off is convenience versus continuity. A second-factor app makes a stolen or guessed password less useful, but it also makes your phone part of the access routine. If your phone is unavailable, the burden shifts to whatever recovery route the account offers. For that reason, I would not finish setup and immediately sign out everywhere. First, confirm that normal login works and that you understand how the account handles a lost or unavailable device.
There is also a useful distinction between installing the app and trusting it with every account. I would add it only where I genuinely need an authenticator, then test each connection separately. This keeps troubleshooting manageable. If one service later fails, you can investigate that service’s registration instead of wondering whether a large collection of accounts was affected.
Small setup choices that save time later
During setup, take note of the exact account context and the method the service tells you to use. Do not rely on memory after closing the page. If the service provides its own recovery instructions, read them before you need them. That is not a criticism of ID.me Authenticator; it is a realistic acknowledgment that second-factor security involves two systems, and the account provider controls much of the surrounding process.
I would also avoid treating a successful first code as proof that every future login will look identical. Services can change their sign-in flow, ask for a different verification method, or require an additional security check. If the next login presents a different screen, follow that screen instead of forcing the old routine onto it.
For people helping a family member, setup is a good moment to explain the difference between a password and an authentication code. The code should be entered only into the legitimate sign-in process that requested it. The app is not a place to share codes with another person who happens to ask for them. That basic explanation is more valuable than simply installing the app on someone’s phone and leaving them to interpret future prompts alone.
Recovering when a login does not work
When a code is rejected, I use a fixed sequence rather than tapping repeatedly. First, I check that the account shown on the login page is the one connected to the authenticator entry. Second, I wait for a fresh code and enter it carefully. Third, I check that I have not accidentally returned to an older login tab or an expired session. This sequence separates an account mismatch from a timing problem.
If the problem continues, I stop generating attempts and return to the account’s security settings or official recovery path. Repeated failures can make the situation harder to understand, particularly if the service temporarily limits sign-in attempts. The authenticator can display the information it has, but it cannot inspect the service’s internal account state.
A useful recovery technique is to restart the process from a clean, current login page while keeping the authenticator installed. I would not remove the app as a first response. Uninstalling may erase local access to the entries you need, and it does not automatically unregister the old setup from the account. Reinstalling is therefore a last resort, not a general troubleshooting button.
If the phone has been replaced, reset, or made unavailable, the correct next step is the account provider’s recovery process rather than trying random registrations in the authenticator. The important question is not simply “how do I get a new code?” but “how does this account verify that I am allowed to register a new device?” That answer belongs to the service connected to the app.
This is where the app’s focused design has a clear limitation. It is easy to understand when everything is already paired, but it offers little help with problems outside that narrow exchange. Someone who expects a complete account-recovery assistant may find the experience frustrating. Someone who understands it as a code-generating part of a wider security system will have more realistic expectations.
Separating phone problems from account problems
Some failures are local to the phone. The app may not open correctly, the screen may be difficult to read, or switching between the login page and the authenticator may be awkward. In those cases, I would close and reopen the relevant screens, check that the phone is functioning normally, and try again without changing the account setup. The goal is to restore a clean workflow without creating a second registration.
Other failures belong to the account or service. A password reset, identity review, locked profile, changed security method, or expired browser session can prevent access even when the authenticator is producing the expected information. If the service rejects the whole sign-in before the second-factor stage, ID.me Authenticator is probably not the part that needs repair.
The same reasoning applies when a login page asks for a different kind of confirmation. Do not assume every two-step prompt accepts an authenticator code. Some services distinguish between codes, approval prompts, text messages, email checks, and other methods. Use the method named by the service. Forcing the authenticator into the wrong prompt is a workflow error, not evidence that the app is broken.
Keeping this separation in mind is one of the most useful lessons from using the app. It prevents the common cycle of reinstalling, re-registering, and trying random codes while the actual issue remains an account-side restriction. A calm diagnosis is faster than a dramatic reset.
How it compares with familiar alternatives
Compared with receiving a code by text message, an authenticator app keeps the second step separate from the phone’s messaging inbox. That can feel cleaner and less exposed to problems involving delayed messages or an unavailable cellular connection. The trade-off is that you must have completed the pairing beforehand and be able to reach the app during login.
Compared with a password manager that also handles authentication, ID.me Authenticator is more limited in scope. That limitation can be welcome if I want a separate tool dedicated to verification and do not need password storage in the same place. On the other hand, people trying to reduce the number of apps they use may prefer an alternative that combines passwords, codes, and recovery organization.
It also differs from a notification-based approval system. A code-based workflow requires me to look at the app and transfer the current information to the login page. That is a little more manual, but it is predictable when notifications are delayed or unavailable. Users who prioritize the fewest possible taps may prefer an approval prompt, while users who want to see the value they are entering may appreciate the directness here.
I would choose this app for a person who wants a free, focused authenticator from ID.me and is comfortable following the connected service’s setup instructions. I would look elsewhere for someone seeking a full password vault, broad identity-management features, or a single place to organize every recovery detail. The app’s narrow purpose is not a flaw by itself; it simply makes the choice depend on how much you want an authenticator to do.
Who should use it and who should skip it
This is a sensible fit for people who regularly sign into an account that specifically supports ID.me Authenticator and want an additional step beyond a password. It is also approachable for less technical users because the everyday action is straightforward once the initial connection is complete. The Everyone age rating and free price make it easy to try without adding a financial barrier.
I would be more cautious recommending it to someone who changes phones frequently, shares devices, or rarely has access to the account’s recovery information. The app cannot remove the responsibility of maintaining access to the device and the connected account. If that responsibility already causes problems with other security tools, a different method may be easier, provided the service supports it.
It may also be the wrong choice for someone expecting the app to verify identity documents, manage passwords, or repair a blocked account. Its role is narrower: it supports the authentication stage. Understanding that boundary before installation is likely to matter more than the app’s simple interface.
My practical verdict
After using it as intended, I see ID.me Authenticator as a focused productivity utility rather than an app you explore for long sessions. Its best quality is that it stays close to one job: helping provide an extra sign-in check. The free model, broad device compatibility, and established user base make it a reasonable option for people whose account workflow calls for it.
The main weakness is not that it tries to do too little; it is that users can easily expect it to solve problems controlled by the connected service. Setup must be completed carefully, account entries must match the login, and recovery needs to be considered before the phone becomes unavailable. Those are meaningful responsibilities, especially for anyone who has never used two-factor authentication.
My recommendation is straightforward: use it when the service you need clearly supports it, test the pairing immediately, and keep the account’s recovery instructions in mind. If a code fails, diagnose the account, timing, login page, and phone separately before reinstalling anything. For a dedicated second-factor tool, it is practical and worth trying; for an all-in-one security manager, it is intentionally not enough.
ID.me Authenticator FAQ
What is ID.me Authenticator and what is it used for?
ID.me Authenticator is a security app that helps protect your ID.me account with multi-factor authentication. After signing in with your password, you may be asked to approve a notification or enter a time-based verification code generated by the app. It is commonly used when accessing government, healthcare, employment, education, and other services that support ID.me sign-in.
How do I set up ID.me Authenticator on my Android or iPhone?
To set up the app, first install ID.me Authenticator from the official Google Play Store or Apple App Store. Sign in to your ID.me account through the security settings, choose the authenticator option, and follow the on-screen instructions. You will usually scan a QR code or enter a setup key, then confirm the generated code before the app becomes an approved verification method.
Does ID.me Authenticator work without mobile data or Wi-Fi?
In many cases, the authenticator can generate time-based security codes without an active internet connection, because the codes are created directly on your device. However, internet access may still be required to complete the initial setup, receive push notifications, or finish certain ID.me sign-in steps. Keeping your phone’s date and time set automatically helps codes remain valid.
What should I do if I lose my phone or cannot access the app?
If your phone is lost, replaced, damaged, or unavailable, you may still be able to access your ID.me account using another registered authentication method, such as backup codes, text-message verification, or an additional trusted device. After signing in, remove the missing device and register a new one. If no recovery option works, use ID.me’s official account recovery and support process.
Is ID.me Authenticator safe, and what permissions does it require?
ID.me Authenticator is designed to add an extra layer of protection beyond your password, making unauthorized access more difficult. The app may request permission to send notifications, particularly when push approval is enabled, while QR-code enrollment may use the camera. Review permissions during installation and only download the official application published by ID.me to avoid counterfeit apps.